A small agency holds a lot of other people’s information: applications, driver and property details, sometimes health or financial data. The law around that information is written for insurers and licensees of every size, and it is not obvious where a five-person agency fits.
IT consulting for insurance agencies answers that in order. First what the rule says, then which systems it touches, then what you would do on the worst day.
A short test, before anything else
The NAIC’s model law is a template. States adopt their own version, sometimes changed, so the model is a guide to the shape of your duties and not the last word. That shape has a useful first question: does the written-program section reach you at all?
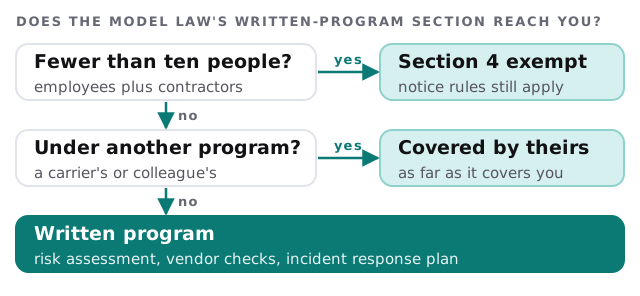
Under the model, a licensee with fewer than ten employees, including independent contractors, is exempt from the information security program section, and so is one covered by another licensee’s program to the extent that it covers them. If neither fits, the model asks for a comprehensive written program based on a risk assessment, commensurate with your size, your activities and how sensitive the data is.
What the work looks like
| Piece of work | What you get | Why it exists |
|---|---|---|
| Rule reading | A page on what your state asks of an agency your size | So decisions rest on the right text |
| Risk assessment | Threats listed, each with likelihood and damage | The model’s starting point for any program |
| Vendor review | One line per vendor: what they hold, who to call | The model’s third-party oversight idea |
| Incident plan | Roles, phone numbers and a first-day checklist | The model asks for a written plan |
| Practice run | A walk through a pretend breach | A plan nobody has rehearsed is only a document |
Your vendors, one at a time
The model asks a licensee to use due diligence in selecting its third-party service providers, and to require them to protect the information systems and data they can reach. In plain terms, you should know who has your clients’ data and what they promised in return.
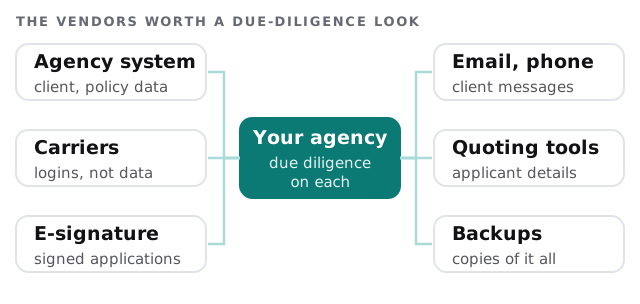
The list tends to turn up surprises. A producer who set up a free scheduling tool that now holds applicant names. A shared mailbox forwarded to a personal address years ago. A scanner that still emails documents to a retired account. None of these is a scandal. Each is a place client data lives that nobody chose on purpose, and the review is where they get a name and an owner.
If you want the day-to-day care side, managed IT services for insurance agencies covers it. For renewals specifically, see insurance renewal reminder automation.
The practice run
The model’s notification rule has a clock: no later than 72 hours from a determination that a Cybersecurity Event has occurred, when its criteria are met. A clock is hard to meet if nobody knows who starts it. We run a short session around four questions.
- Who decides that something is a reportable event? A named person, with a named backup.
- Who calls your carriers, your counsel and your insurer? In what order, using which numbers?
- Where are the records of what was affected? Access logs, backups, the vendor’s contact.
- Who tells the staff, and what do they say? One voice, written beforehand.
None of this requires technology. It requires having thought about it once, on a calm day.
The model law doesn’t ask small agencies to be perfect. It asks them to know their data, their vendors and who to call.
What we need from you
- The number of people in the agency, counting contractors.
- A list of every system that touches client data, including the ones used by one producer.
- Your state’s current text, or the name of whoever interprets it for you.